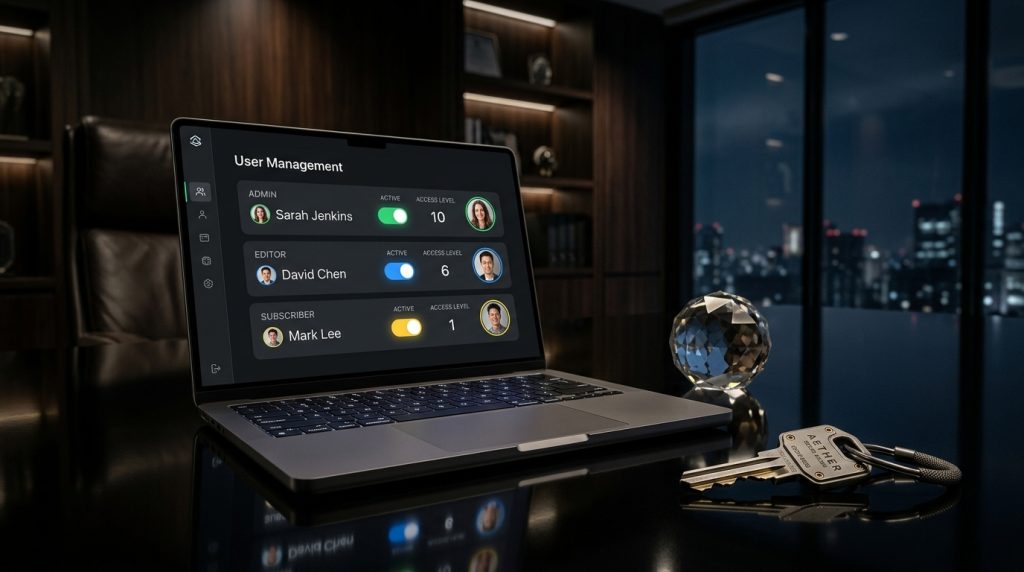
WordPress comes with a built-in user role system that controls what different users can do on your site. Administrators can do everything. Contributors can do very little. Between these extremes are several intermediate roles.
For sites with one user, roles do not matter much. For sites with multiple contributors, editors, or team members, roles become essential. The right role assignments protect the site from mistakes and limit the damage from any compromised account.
This piece covers the default WordPress roles, when to use each, and how to extend the role system for specific needs.
The Default WordPress Roles
WordPress includes five main roles.
Administrator
Full access to everything. Administrators can install and delete plugins and themes, manage users, change site settings, edit any content, and modify code through the theme and plugin editors.
Administrators are the most powerful users. Any admin account, if compromised, gives an attacker full control over the site.
Limit administrator accounts to people who genuinely need this level of access. For most sites, this means the site owner and possibly one or two trusted people.
Editor
Manages content from all users. Editors can publish, edit, and delete posts and pages from any user. They can manage comments, categories, and tags.
Editors cannot manage users, install plugins or themes, or change site settings.
Good for senior content managers who need to oversee all content but do not need to manage the technical aspects of the site.
Author
Manages their own content. Authors can write, edit, publish, and delete their own posts. They can upload files.
Authors cannot edit content created by other users, cannot manage pages (only posts), cannot manage other users, and cannot change site settings.
Good for individual writers on a multi-author blog.
Contributor
Can write posts but cannot publish them. Contributor posts go to editors for review before being published. Contributors can edit their own posts but only until they are published.
Contributors cannot upload files. They cannot access media except what is inside their posts.
Good for guest writers or junior contributors who need editorial oversight.
Subscriber
Minimal access. Subscribers can view their own profile and change their password. They cannot create content.
Useful for sites that require registration for accessing certain content but do not want users to contribute.
Additional Roles from Popular Plugins
Some plugins add their own roles.
Shop Manager (WooCommerce)
WooCommerce adds a Shop Manager role. Shop Managers can manage all aspects of the store. Products, orders, coupons, reports.
Shop Managers cannot access unrelated WordPress admin areas or install plugins.
Good for staff who manage the e-commerce operations without needing full site admin access.
Customer (WooCommerce)
WooCommerce adds a Customer role. Customers can view their own account, orders, and addresses.
Customer accounts are created when someone checks out on a WooCommerce site.
Various Membership Roles
Membership plugins often add roles for different membership levels. These roles control access to member-only content.
Course-Specific Roles
Learning management system plugins like LearnDash add roles for instructors, students, and other course-related positions.
When to Use Each Role
Matching roles to actual needs matters.
For the Site Owner
Administrator. This is the one user who needs full access.
For sites with multiple owners, each may need administrator access.
For Senior Content People
Editor. Handles content management without giving access to site configuration or user management.
For Content Writers
Author for regular writers. Contributor for writers who need editorial review before publishing.
The choice depends on whether you want their content published immediately or reviewed first.
For Non-Content Team Members
Custom roles or specific plugin roles may fit better than the default roles. A marketing person might need access to marketing tools without needing full editor access.
For Members
Subscriber for basic members. Custom membership levels for tiered access.
For Store Staff
Shop Manager for staff who need e-commerce admin access.
For Customers
Customer role (from WooCommerce) for people who buy from the store.
Custom Roles
When default roles do not fit, custom roles help.
When to Create Custom Roles
When your team has specific responsibilities that do not match default roles. A marketing manager who needs access to marketing plugins but not content editing. A support person who can view orders but not modify them.
Custom roles let you precisely define what each type of user can do.
How to Create Them
Several plugins handle custom role creation.
Members plugin from MemberPress team lets you create and edit roles visually.
User Role Editor is another popular option.
PublishPress Capabilities focuses on managing capabilities across roles.
These plugins let you create new roles and specify exactly what each can do.
Capabilities
Roles are collections of capabilities. Individual capabilities are things like “edit_posts” or “manage_options.”
You can add or remove specific capabilities from any role, including default roles. This provides fine-grained control.
Cloning Existing Roles
Often the easiest way to create a custom role is to clone an existing one and modify it. Start with the closest default role, then adjust.
Managing Users
The daily work of user management.
Adding Users
Under Users > Add New in the WordPress admin. Enter username, email, name, and password. Assign a role.
For sites with self-registration enabled, users create their own accounts.
Editing User Roles
Users can be changed to different roles at any time. Under Users, edit a user and change their role.
Be careful about changing roles. Downgrading a user might remove their access to their own content. Upgrading grants more capabilities.
Removing Users
Users can be deleted when they no longer need access. When deleting, WordPress asks what to do with their content. Delete it or reassign to another user.
For departing team members, reassigning content is usually the right choice.
Bulk Actions
The Users screen supports bulk actions. Change roles, delete users, or send password resets in batches.
Security Considerations
User roles affect security significantly.
Least Privilege Principle
Give each user the minimum access needed for their job. Not more. Not less.
The earlier piece in this series covered user permissions from a security perspective.
Limit Admin Accounts
Every admin account is a potential entry point for attackers. Fewer admin accounts means smaller attack surface.
For most sites, one or two admin accounts is enough.
Regular Audits
Review the user list periodically. Remove accounts for people who no longer need access. Downgrade users who have more permissions than they need.
Old accounts accumulate. Regular cleanup keeps user access aligned with current needs.
Strong Passwords Required
Enforce strong passwords for all users, especially those with elevated permissions. Weak admin passwords are a common vulnerability.
Two-Factor Authentication
Enable 2FA for admin accounts. Consider requiring it for editors and other elevated roles too. Earlier pieces in this series covered 2FA in detail.
Common Role Management Mistakes
Users stumble in predictable ways.
Everyone Is an Administrator
The biggest mistake. Making all users administrators for convenience. This creates massive security risk.
Assign roles appropriately based on actual needs.
Not Cleaning Up Old Accounts
Accounts for departed employees or completed contractors stay active. Each is a potential entry point.
Set up a process to remove access when people leave.
Shared Accounts
Multiple people using the same account. This defeats audit logging and creates security issues.
Each person should have their own account.
Not Understanding Capabilities
Assigning roles without understanding what they can do. Sometimes editors have more capability than expected. Sometimes contributors have less than expected.
Verify roles match your intent.
Default Admin Username
Sites still using “admin” as the username make brute force attacks easier. Change to a different username.
Weak Passwords Allowed
Not requiring strong passwords lets users pick weak ones. Enforce policies.
Working with Roles in Plugins
Some plugins add capabilities that interact with roles.
User Role Editor
Comprehensive plugin for managing roles and capabilities. Add, edit, delete roles. Modify what each role can do.
Members
Also handles role management with a clean interface.
PublishPress Capabilities
Focused on capability management. Good for detailed control over what each role can do.
Restrict Content Pro & Similar Membership Plugins
Membership plugins add their own permission systems that work alongside WordPress roles.
WooCommerce
WooCommerce adds the Shop Manager and Customer roles automatically. It also adds capabilities to existing roles.
Learning Management Systems
LMS plugins add roles for instructors, students, and administrators of the learning system.
Reporting & Auditing
Understanding who does what on your site.
Activity Log Plugins
Plugins like WP Activity Log, Stream, and Simple History track what users do on your site. Login events, post edits, plugin activations, settings changes.
These logs help investigate incidents and understand user activity.
User Access Reports
Some plugins provide reports on user access patterns. When users last logged in. What they accessed. What changes they made.
Useful for security audits and access reviews.
Wrapping Up the Access Management Picture
WordPress user roles are one of those features that gets overlooked until they matter. Sites with proper role management handle security and team coordination better than sites where everyone is an administrator.
For most sites, the default WordPress roles handle basic needs. Administrator for the owner. Editor for senior content people. Author for writers. Contributor for occasional contributors. Subscriber for basic members.
For more sophisticated needs, custom roles or plugin-provided roles fill gaps. E-commerce sites use Shop Manager. Membership sites use various membership levels. Complex organizations use custom roles that match their specific team structures.
The security implications of role management are significant. Every admin account is a potential vulnerability. Every unnecessary permission is potential damage. Applying least privilege consistently protects the site.
For sites without deliberate role management currently, an audit is worthwhile. Look at every user. Consider what they actually need. Adjust roles to match. Remove accounts that are no longer needed.
For sites with proper role management already in place, periodic review keeps things aligned with current needs. Team members change roles within the organization. Contractors finish projects. Employees leave. Roles need to keep up with these changes.
Good user management is one of those things that seems tedious until you need it. Then it becomes essential. The investment in proper role management pays back through security incidents that stay contained, teamwork that runs smoothly, and access that matches actual needs. Take role management seriously, and your WordPress site has a foundation for handling growth and team changes cleanly.